Data & confidentiality
Classification, minimization, secrets and control of information transmitted to models.
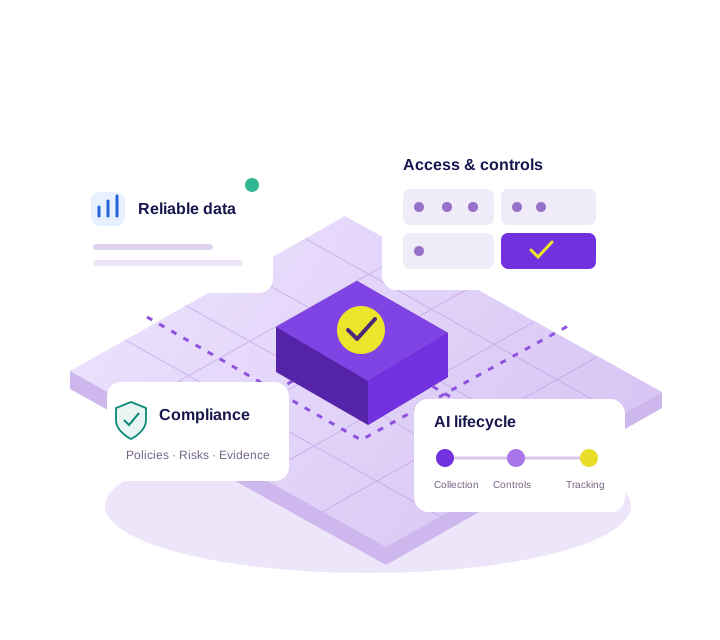
Reliable data. Mastered AI uses.
Structure your data, protect your AI systems and prepare your compliance approach. Our consultants and technical experts work with your business lines, your IT department and your risk teams.
Data Management · AI Security · ISO/IEC 42001
01 / Data
Reliability, traceability and access: we are building the Data base that allows you to exploit your information and industrialize your AI uses.
We evaluate your Data Management practices, your processes and the data sets necessary for the chosen uses. DMMA diagnosis is based on DAMA-DMBOK.
DeliverablesMaturity diagnosis, mapping of critical data, risks and target vision.
We organise the responsibilities of data owners, quality referents and technical teams, with the associated decision circuits and policies.
DeliverablesData organisation, roles and responsibilities, policies and governance bodies.
We define the checks for accuracy, completeness, freshness and consistency, then the rules for managing the reference data.
DeliverablesQuality programme, Master Data strategy, benchmarks and monitoring indicators.
Sources, metadata, classification and transformations are documented to follow the journey of the data to its business and AI uses.
DeliverablesData catalog, classification rules and mapping of flows and transformations.
Collection, cleaning, transformation and annotation: we prepare structured and documentary data, evaluate bias and distinguish learning, evaluation and production.
DeliverablesDocumented datasets, annotation rules, quality checks and reproducible pipelines.
Data projects are prioritised according to the business needs, dependencies and capabilities of your teams. The trajectory can cover 24 to 36 months, depending on the scope.
DeliverablesPrioritised roadmap, operational data model, planning and dashboard.
Scope, actors and priority data.
Maturity, irritants and Data Management target.
Projects, governance and indicators.
02 / Security
We assess the risks of your applications, their data and their actions. The controls are adapted to their criticality and their level of autonomy.
Classification, minimization, secrets and control of information transmitted to models.
Authentication, limited privileges, service accounts and API key protection.
Evaluation of prompt injections, information leaks and control overrides.
Hosting, dependencies, contractual commitments and data processing conditions.
Exploitable traces, alerts and human control of sensitive actions.
Escalation procedures, controlled shutdown and resumption of operations.
Risk mapping, test results, remediation plan and operating rules.
AI at the service of cyber teams
AlertsGroup, enrich and prepare for sorting.
VulnerabilitiesReconcile assets, create tickets and track corrections.
ReportingCollect evidence and prepare summaries for validation.
03 / Compliance
We support you in setting up an AI management system: responsibilities, risks, controls and proof of operation.
We define the scope of the AI management system, identify stakeholders and review your existing processes and documents.
DeliverablesGap analysis and prioritised action plan.
Technical and organisational risks and impacts on people are studied according to the systems concerned, with the treatment measures and responsibilities.
DeliverablesRisk register, impact assessments and treatment plan.
We structure the AI policy, roles, objectives and documentation of the management system, articulating it with your quality and safety practices.
DeliverablesAI policy, procedures, responsibilities and documentary models.
Design, testing, validation, deployment and monitoring: controls are integrated into projects. The teams are made aware of the responsibilities and authorized uses.
DeliverablesDocumented controls, validation criteria and training plan.
We support you in the internal audit programme, monitoring of indicators, management review and handling of non-conformities.
DeliverablesAudit programme, dashboard and corrective action plan.
We prepare the mock audit and the evidence file, then the actions to be carried out before the external audit. Certification is issued by an independent certification body.
DeliverablesPreparation file, results of the mock audit and monitoring plan.
We map the requirements applicable to your activities and countries of operation, with your legal, compliance and security functions. Purposes, access, conservation and traceability are integrated into the processes.
Indicators, management reviews and corrective actions allow your management system to evolve with your AI uses.
Reference: ISO/IEC 42001:2023 — AI management systems.
What you get
A mission targeted on data, security or compliance; the three components can be mobilized separately.
Illustrative structures. The documents and their scope are adapted to your mission.
Concrete uses that mobilize architecture, access control, traceability and management.
Legal agents on the bank's infrastructure, with open models, human validation and traceability of actions.
See the customer case
Audit of the national Data and AI index: consistency of indicators, contribution of initiatives and maturity trajectory.
See the customer caseNo. The mission may relate to a Data need, an AI system to be secured or preparation for ISO/IEC 42001. The framework identifies the dependencies and the experts to be mobilized.
Yes. We start from your IS, your data and your practices. The choices of tools and hosting are studied according to your integration, confidentiality and operating constraints.
An independent certification body, following its audit. AI Crafters supports you in the preparation, implementation of requirements and handling of deviations.
Let’s discuss your project
Data diagnostics, securing AI uses or preparing for ISO/IEC 42001: our experts help you frame the mission.